All three items this week are about boxes that sit quietly in a closet or a server room until something goes wrong. Ivanti shipped a second round of fixes for its Connect Secure VPN, so the October patch alone is no longer enough. Synology says attackers are encrypting NAS devices that missed updates from late 2024. And a GitLab flaw that was patched in October is now on CISA's list of bugs being used in real attacks.
If your Milwaukee or Southeast Wisconsin office has a VPN appliance, a NAS, or a code server that nobody has logged in to for a while, this is the week to check on it.
Ivanti Connect Secure: the October patch is not the end, install 25.1.1.3 or 22.8R2.6
What happened
On October 13, Ivanti patched CVE-2026-104935, an authentication bypass in Connect Secure that was already being exploited. We covered it in our October 14 threat brief. On October 29, Ivanti updated the same advisory with two more flaws that attackers were chaining with it: CVE-2026-111357, which lets a logged-in attacker escalate privileges, and CVE-2026-118527, which lets an authenticated attacker upload files with their own content to a known spot on disk. Ivanti says it is "aware of exploitation in the wild affecting a limited number of customers at the time of disclosure when CVE-2026-104935, CVE-2026-111357 and CVE-2026-118527 are chained." (Ivanti advisory) CISA added both new CVEs to its Known Exploited Vulnerabilities catalog on October 30.
CISA says the chain "allows remote, unauthenticated execution of arbitrary commands" and that attackers have used it for credential theft and data exfiltration. (CISA alert)
Who is affected
Offices that use Ivanti Connect Secure for remote access and run one of these versions, per Ivanti's advisory:
- 25.1.1.2 and earlier
- 22.8R2.5 and earlier
Ivanti says 22.7.x and earlier do not contain these flaws, and 25.1.3.0 (on the ISA4500, ISA6500, or ISA8500 platform) and later do not either.
What to check or fix now
- Find out which Connect Secure version you run. If you installed the October fix (25.1.1.2 or 22.8R2.5), you still need this update.
- Upgrade to 25.1.1.3 or 22.8R2.6. Ivanti recommends 25.1.1.3 for 22.8 customers and offers 22.8R2.6 for those who cannot move to 25.1 yet.
- Do not treat a clean Integrity Checker result as proof. CISA notes the tool "may not detect evidence of exploitation of CVE-2026-104935 because threat actor commands execute in memory."
- If you suspect the appliance was compromised, CISA's alert lists recovery steps, including resetting passwords for all domain, administrator, and local accounts, and revoking and reissuing stored certificates and API keys.
How to prevent it
Plan the move to 25.1 now. Ivanti says both 22.7 and 22.8 reach end of life on January 31, 2027, and moving to 25.1.3.0 needs the new ISA4500, ISA6500, or ISA8500 platform. For virtual or cloud devices, that means building new appliances from the 25.1.3.0 template. That is a project, not a patch, so budget the time before it becomes urgent. For why a steady update routine matters, see why software updates are your first line of defense.
Synology NAS: ransomware is hitting devices that missed old DSM updates
What happened
On October 29, Synology said it "has identified threat actors exploiting a vulnerability patched in December 2024 to target devices running outdated versions of DSM. These attacks aim to encrypt data and extort ransom." (Synology statement) Synology's US announcement adds that the threat targets devices running end-of-life DSM versions. Synology points to its advisory Synology-SA-24:20 for details.
In the same announcement, Synology said its PHP2Shell investigation found the PHP flaws only affect systems running certain PHP-based packages, and it released PHP updates for DSM 7.4 and 7.3 as well as the end-of-life DSM 7.2, 7.1, 7.0, and 6.2.
Who is affected
- Any Synology NAS running a DSM version older than the fixes in Synology-SA-24:20. That advisory lists, for example, DSM 7.2.2-72806-1, 7.2.1-69057-6, 7.2-64570-4, 7.1.1-42962-7, and 6.2.4-25556-8 as the minimum fixed builds.
- For the PHP issue: devices running Calendar, IDrive, Joomla, KodExplorer, MailStation, MediaWiki, phpMyAdmin, vtigerCRM, Web Station, or WordPress. Synology says Synology Drive is not affected by PHP2Shell.
What to check or fix now
- Sign in to DSM and install the newest DSM update offered for your model. The versions in SA-24:20 are the floor, not the goal.
- Turn on automatic DSM updates, which Synology recommends.
- If you use any of the packages listed above, update PHP in Package Center. Synology says MailStation needs a manual update.
- If your DSM version is older than 6.2, Synology recommends temporarily disabling the affected packages until you move to a supported DSM version.
- If a NAS is already encrypted, Synology says it cannot decrypt the data. Its recovery guidance is a factory reset, a DSM reinstall, and a restore from backup.
How to prevent it
Do not leave the DSM sign-in page open to the internet. Use a VPN for remote access instead of a port forward on the router. And keep at least one backup copy somewhere the NAS cannot write to. Ransomware that encrypts the NAS can also encrypt backups stored on the same NAS. To put numbers on what a locked-up NAS would cost your office, see what would a ransomware attack cost you, and for building a recovery plan around it, see disaster recovery and business continuity planning.
Self-managed GitLab: the October critical bug is now being exploited
What happened
On October 12, GitLab released versions 19.4.2, 19.3.5, and 19.2.8 to fix CVE-2026-97229, a critical flaw rated 10.0. It could let an unauthenticated user run code on the GitLab server through a specially crafted regular expression in a CI/CD configuration. CISA added it to the Known Exploited Vulnerabilities catalog on October 29.
Who is affected
Self-managed GitLab Community Edition and Enterprise Edition, from 19.2 before 19.2.8, 19.3 before 19.3.5, and 19.4 before 19.4.2. GitLab says GitLab.com and GitLab Dedicated are already patched. That includes GitLab running in a container on a NAS or a small server, which is easy to forget about.
What to check or fix now
- Find every self-managed GitLab instance, including test servers and containers.
- Upgrade to the latest patch release for your version, at minimum 19.4.2, 19.3.5, or 19.2.8. GitLab notes 19.3.4 had a merge request bug that 19.3.5 fixes.
- If you cannot upgrade today, take the GitLab web interface off the internet until you can.
- CISA's catalog entry notes that other software built on the same Ruby regular expression code may also be affected, so ask vendors of other Ruby-based tools whether they need an update.
How to prevent it
Keep a list of self-hosted apps and who patches each one. Tools that a developer or vendor set up once are the ones that fall behind, and an internet-facing code server can hold passwords, API keys, and deployment secrets.
What to do this week
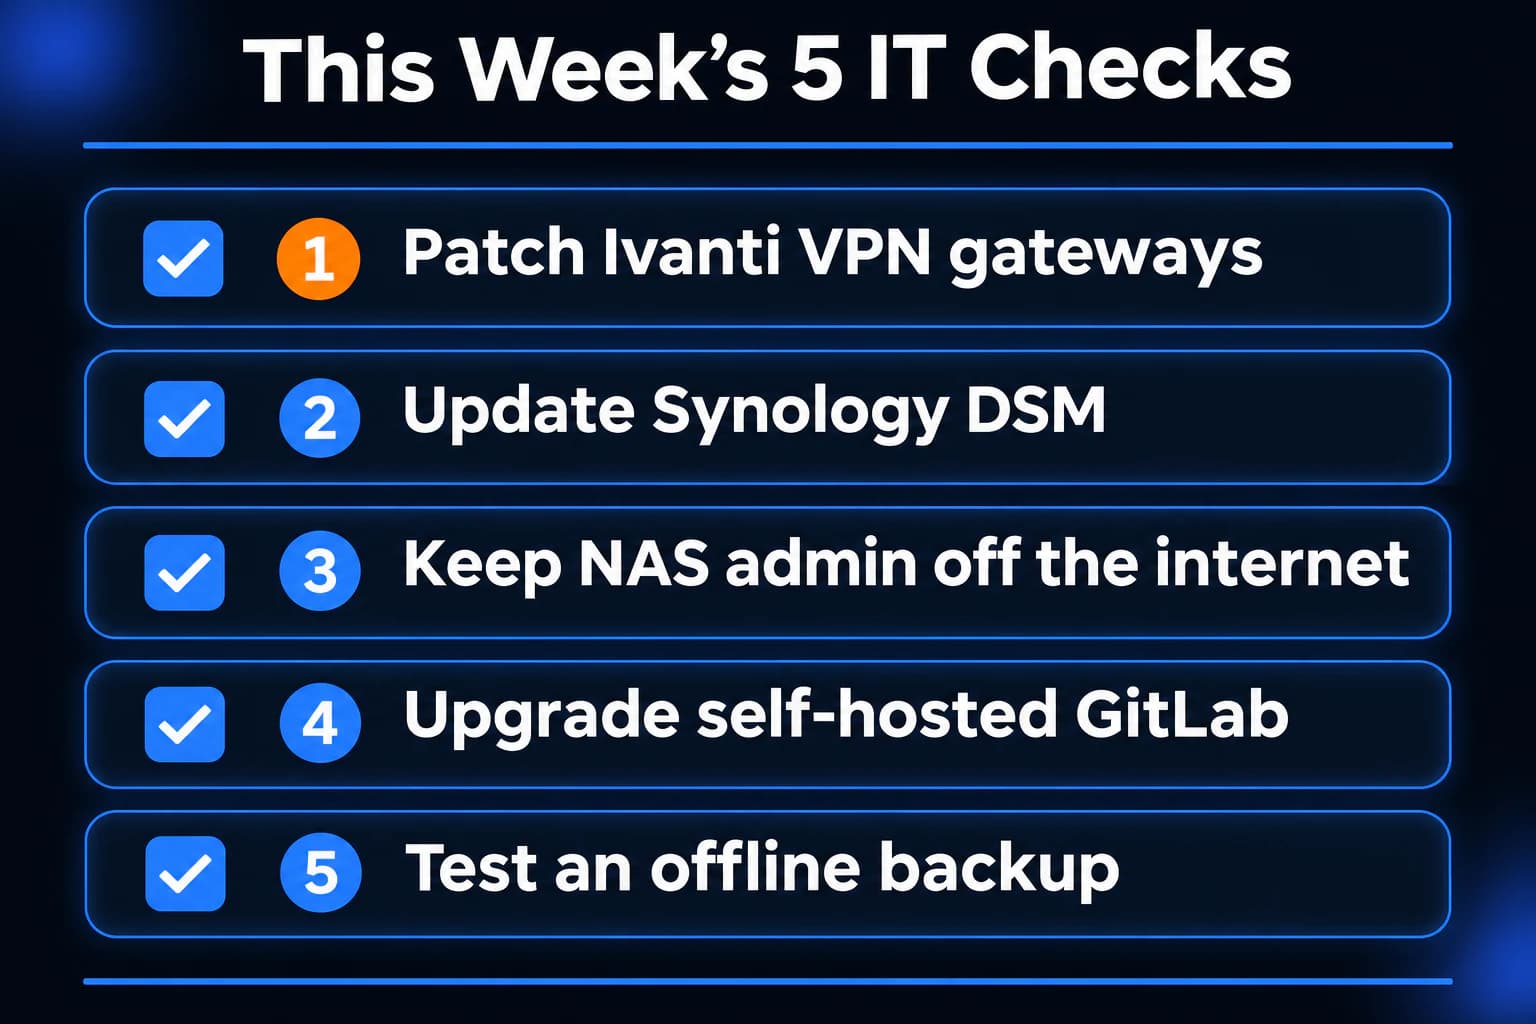
- If you use Ivanti Connect Secure, upgrade to 25.1.1.3 or 22.8R2.6, even if you patched in October.
- Install the newest DSM update on every Synology NAS and turn on automatic updates.
- Update PHP in Package Center on any Synology NAS running Web Station, WordPress, Calendar, MailStation, or the other listed packages.
- Upgrade self-managed GitLab to 19.4.2, 19.3.5, 19.2.8, or later, and keep NAS and GitLab admin pages off the open internet.
- Restore one file from a backup copy that your NAS and servers cannot write to, so you know it works.
If you need someone who can handle these checks for you, reach out to us. We would be happy to help. See how we handle backup and disaster recovery and managed security services for offices around Milwaukee.
Sources
- Ivanti Security Advisory, Connect Secure (CVE-2026-104935), updated October 29
- CISA alert on Ivanti Connect Secure, updated October 30
- CISA adds two Known Exploited Vulnerabilities, October 30
- NVD, CVE-2026-104935
- NVD, CVE-2026-111357
- NVD, CVE-2026-118527
- Synology, October 29 statement
- Synology US announcement, PHP2Shell fixes for older DSM releases
- Synology-SA-24:20
- Synology Knowledge Center, recovering a NAS after ransomware
- GitLab Critical Patch Release 19.4.2, 19.3.5, 19.2.8
- NVD, CVE-2026-97229
- CISA Known Exploited Vulnerabilities catalog entry, CVE-2026-97229

Powerful IT Systems · Sussex, WI
Hands-on IT experience serving Milwaukee-area businesses.